RegTech and compliance software your regulator can follow
AML transaction monitoring, sanctions and PEP screening, regulatory returns, GRC and audit readiness, complaints handling and KYB case management. Built so every decision has an owner, a reason and a deadline.
What RegTech and compliance software has to get right
Compliance teams are judged on what they can prove. The problems we see are alerts nobody can work through, returns rebuilt in spreadsheets every quarter, and evidence for audits collected by hand from a dozen tools.
The builds below turn that work into cases with owners, rules with versions, and deadlines on the record. Four-eyes approval sits on the decisions that matter, and the audit trail is a by-product of doing the work.
Problems we are asked to fix
The problems teams bring to us, the system that fixes each one and the builds that did it.
AML transaction monitoring
Rule-based AML monitoring raises too many alerts to review.
Alerts, cases and suspicious activity report deadlines in one system, with rules tuned and versioned.
Sanctions and PEP screening
Name screening against sanctions and PEP lists produces noisy matches.
Matching tuned to cut false positives, with four-eyes decisions on true matches and every decision logged.
Regulatory reporting platform
Regulatory returns are built in spreadsheets every quarter.
Returns built from source data with checks, sign-off and a full trail from each number back to its source.
GRC and audit readiness
Evidence for audits is collected by hand from many tools.
Controls, risks and evidence tracked in one place, with evidence pulled from the tools that hold it.
Complaints management
Complaints miss regulatory deadlines because they are tracked in inboxes.
Every complaint on the regulator's clock, with letters, escalations and outcomes logged.
KYB case management
Business customer due diligence needs ownership checks across registries.
Company registry lookups, ownership tracing to beneficial owners and four-eyes approval in one case.
7 kinds of RegTech and compliance system we have built
Each one links the product build behind it, counted from our case studies.
RegTech and compliance products we built
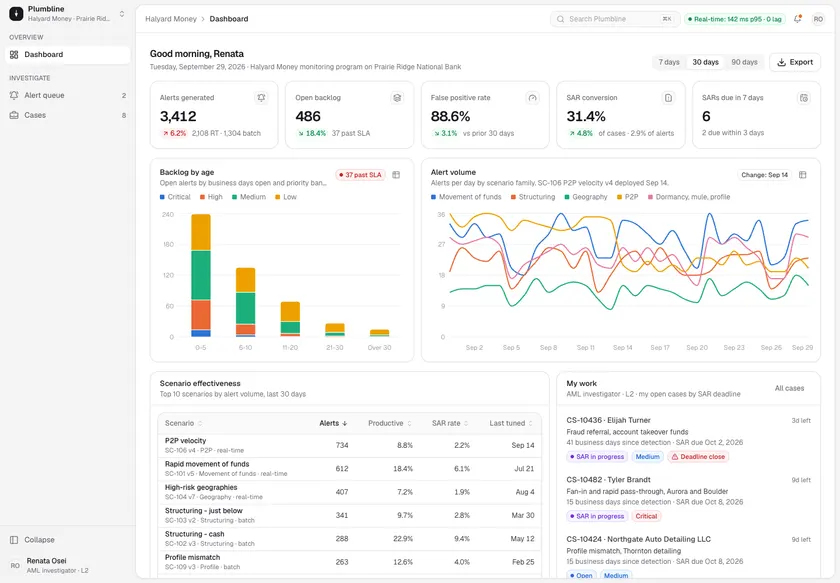
Plumbline - AML Transaction Monitoring with Alerts, Cases and SAR Deadlines in One System
Designed and built a clickable AML transaction monitoring system for a US neobank and its sponsor bank: scenario alerts ranked by a transparent priority score, an investigation workspace that shows why each alert fired, real-time payment holds, and cases that count down to the SAR filing deadline.
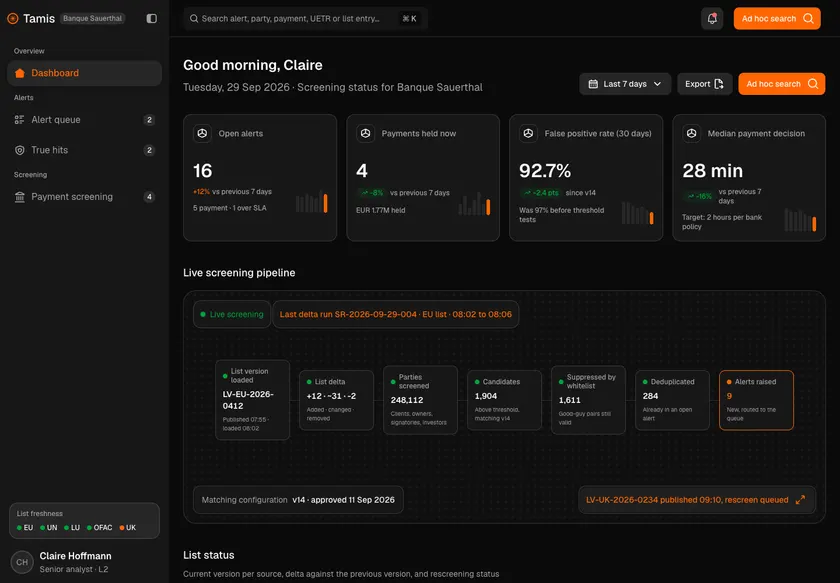
Tamis - Sanctions and PEP Screening Platform with Four-Eyes Decisions
Designed and built a clickable sanctions and PEP screening platform for a Luxembourg private bank and fund administrator: rescreening as soon as a list changes, a payment hold queue against currency cut-offs, side-by-side alert review with four-eyes approval, and true hit cases that track the freeze and every report to the authorities.
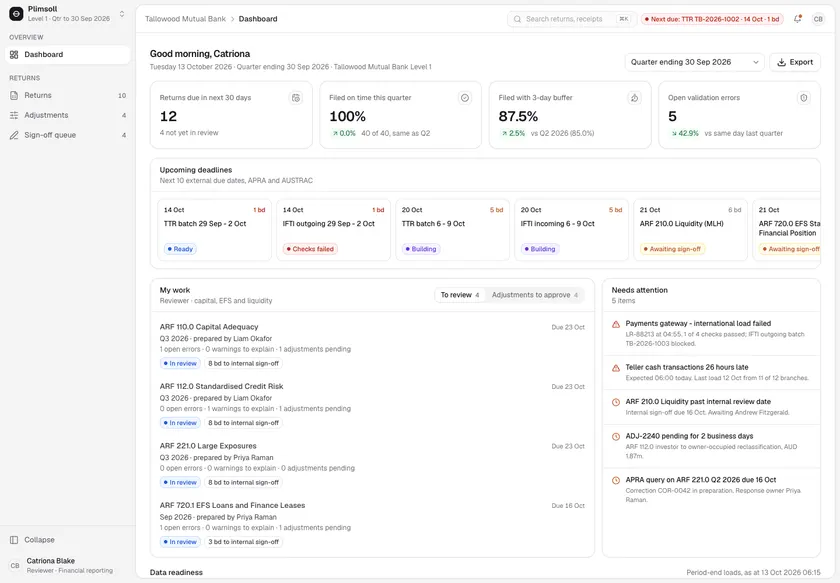
Plimsoll - Regulatory Reporting Platform for APRA and AUSTRAC Returns
Designed and built a clickable regulatory reporting platform for an Australian customer-owned bank: prepare APRA returns from core banking and general ledger data, clear validation errors, comment on variances, approve adjustments within policy limits and sign off against an evidence pack, with every reported number traceable to its source.
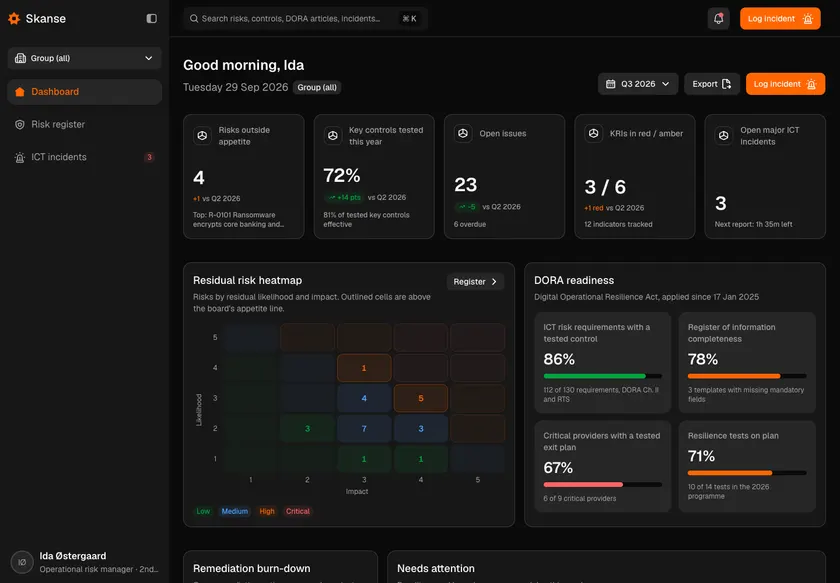
Skanse - GRC Platform for Risk, Controls and DORA Incident Reporting
Designed and built a clickable GRC platform for a Danish bank and pension group: a risk register scored inherent and residual against the board's appetite, a dashboard with DORA readiness, and an ICT incident log that classifies incidents against the DORA criteria and runs the reporting clock to Finanstilsynet.
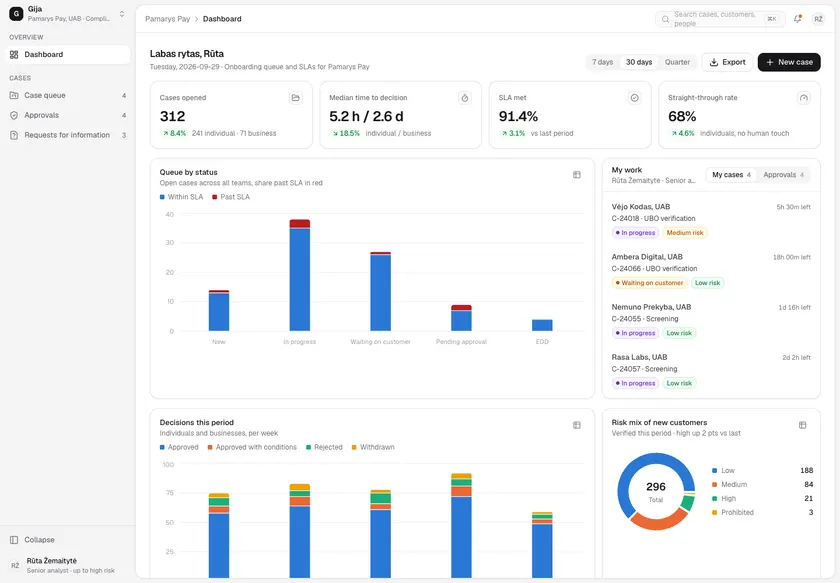
Gija - KYC and KYB Case Management with Ownership Tracing and Four-Eyes Approval
Designed and built a clickable KYC and KYB case-management platform for a Vilnius electronic money institution: a case queue with SLAs, individual and business cases with registry comparison and beneficial ownership traced through every layer, an explainable risk score, four-eyes approval and requests for information sent to customers.
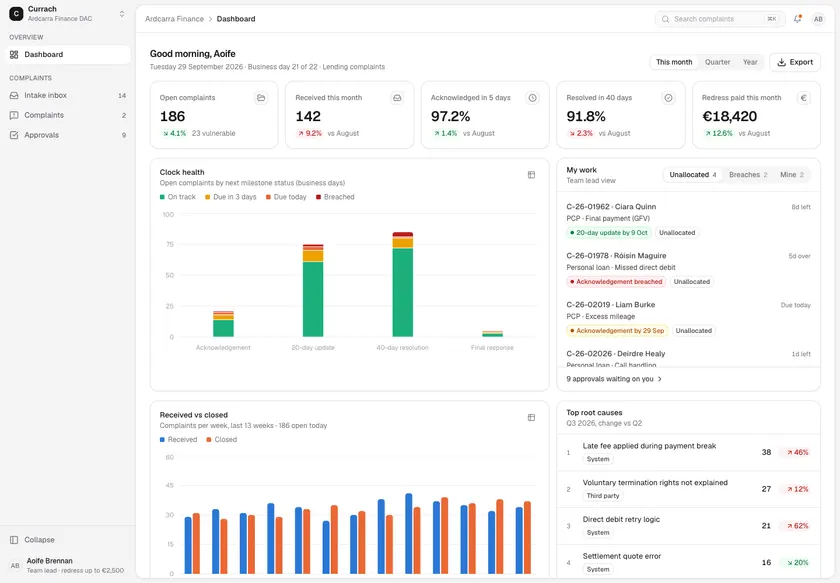
Currach - Complaints Management on the Consumer Protection Code Clock
Designed and built a clickable complaints management system for an Irish lender of personal loans, home improvement loans and car finance: one intake inbox for every channel with an explicit complaint test, a business-day clock on the Irish calendar, a complaint workspace with root-cause tagging, and an approvals queue where final letters carry locked FSPO wording.
The rules involved
The rules this kind of software usually has to follow. Guidance, not legal advice.
- 01
Anti-money laundering
The Bank Secrecy Act in the US, the EU AML directives and the new EU AML Regulation, and national AML laws, which set monitoring, reporting and due diligence duties.
- 02
Sanctions
EU, UK, UN and US sanctions lists, which firms must screen customers and payments against.
- 03
Operational resilience
DORA in the EU, and national rules such as those of APRA in Australia, set ICT risk and incident duties.
- 04
Regulatory reporting
Each regulator sets its own returns, formats and deadlines.
- 05
Consumer protection
Complaints handling rules and deadlines set by financial regulators and ombudsman schemes.
Framework guides
Rules our RegTech and compliance builds cite most
- GDPR5
- ISO/IEC 27001:20222
- AML/CTF Act 20061
- AML/CTF Amendment Act 20241
- Anti-structuring (31 U.S.C. 5324)1
- APRA reporting standards (ARS)1
- APS 3101
- Assisted Decision-Making (Capacity) Act 20151
- Bank Secrecy Act1
Two ways to work with OceanLab
Project build
We design and build the system as one project. It starts with a clickable prototype your team tries before any production code is written. Pay per milestone (outcome-based) or hourly at $30-50/hr, depending on role and seniority.
Embedded engineers
Our engineers join your team on a flexible monthly retainer. Part-time is fine and it runs month to month, with hours that overlap the US, UK and Europe, the Middle East, and Australia and Asia. Outcome-based or $30-50/hr.
Guides and tools
RegTech and compliance software questions
Can you reduce false positives in our monitoring?
Usually, by tuning rules on your own data, adding context to each alert and scoring alerts by risk. Every change is versioned and tested, so you can show your regulator why a rule changed.
Can AI decide AML cases?
We use it to gather context and draft narratives for an analyst. The decision to close or report stays with a person, and the reasons are kept on the case.
Do you build for more than one regulator?
Yes. The builds here cover rules in the US, Ireland, Luxembourg, Lithuania, Denmark, Israel and Australia. Rules and returns are configuration, so new ones can be added.
