HIPAA compliance checklist for software teams
Work through every Security Rule safeguard with its citation and what it means for your code, then export your progress.
Free, runs in your browser, no sign-up. Updated 2026-10-25.
Guidance, not legal advice. This checklist helps engineering teams plan; your compliance officer or counsel decides what applies to you.
0 of 45 done, 0%.
- Required done
- 0 of 23
- Administrative safeguards (164.308)
- 0 of 22
- Physical safeguards (164.310)
- 0 of 10
- Technical safeguards (164.312)
- 0 of 9
- Policies and documentation (164.316)
- 0 of 4
Ask OceanLab to help close the gaps
Opens an email to OceanLab with this result and a link to your inputs. Nothing is sent until you press send, and there is no sign-up.
How this is calculated
The list follows 45 CFR Part 164 Subpart C, the HIPAA Security Rule, as published on eCFR on the checked date: administrative, physical and technical safeguards, plus policies and documentation.
Each item keeps its citation and its Required or Addressable label from the rule. The 'in code' line is OceanLab's plain-English reading for engineering teams.
Your ticks are saved in this browser only. Export them as Markdown or print the page.
Sources
- 45 CFR Part 164, Subpart C (Security Rule), eCFR · checked 2026-10-23
- 45 CFR Part 164, Subpart D (Breach Notification), eCFR · checked 2026-10-23
Questions about this tool
What does Addressable mean?
You must assess whether the safeguard is reasonable for you. If it is, implement it; if not, document why and use an equivalent measure. It does not mean optional.
Which version of the rule is this?
The Security Rule text in force on eCFR on the checked date. Proposed changes are not included until they are final.
Does a HIPAA-eligible cloud make my app compliant?
No. The provider covers its own infrastructure under a business associate agreement. Access control, audit logs and encryption in your app are still your job.
Is this legal advice?
No. It is guidance for engineering teams. Your compliance officer or counsel decides what applies to you.
Other free tools
OceanLab product builds like this
Products OceanLab designed and built. Each case study covers the screens, the scope and the rules it was built for.
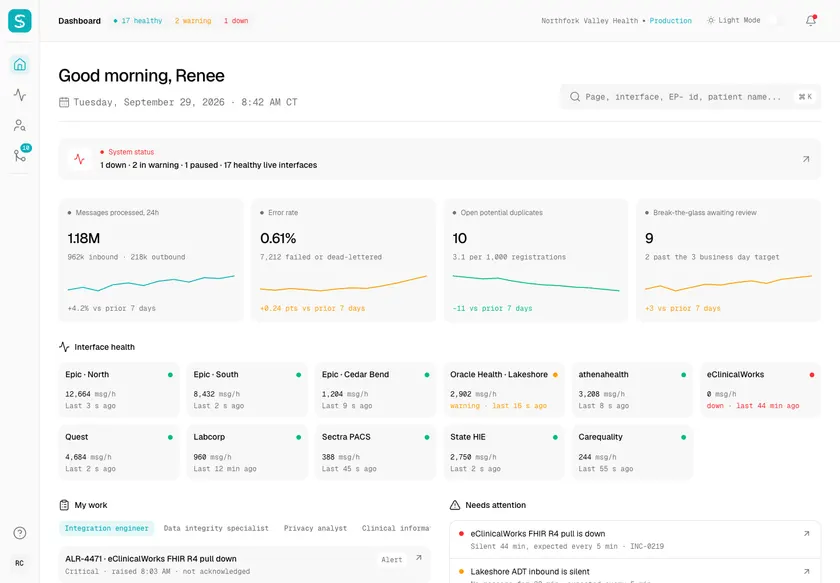
Sutura - HIPAA-Compliant Patient Data Hub over HL7 and FHIR
Designed and built a clickable patient data hub for a US health system running Epic, Oracle Health, athenahealth and eClinicalWorks: a live monitor for every HL7 v2, FHIR and HIE feed, one matched enterprise patient with a provenance-tagged record, and a duplicates queue where a person decides every uncertain match.
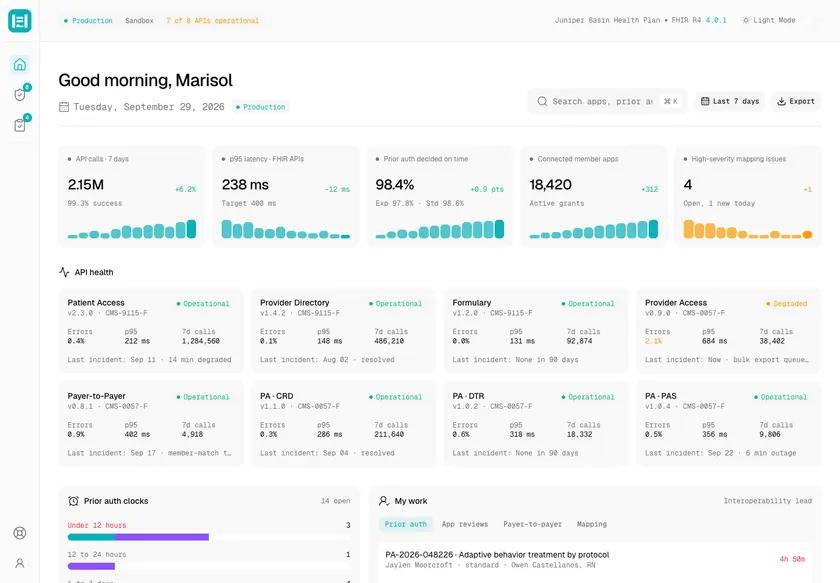
Headgate - FHIR Interoperability API Platform for Claims, Clinical Data and Prior Authorization
Designed and built a clickable console for the FHIR APIs a US regional health plan must run under federal interoperability rules: API health across Patient Access, Provider Directory, Formulary, Provider Access, Payer-to-Payer and Prior Authorization, a security review queue for third-party apps, and one clock for every prior authorization request, however it arrived.
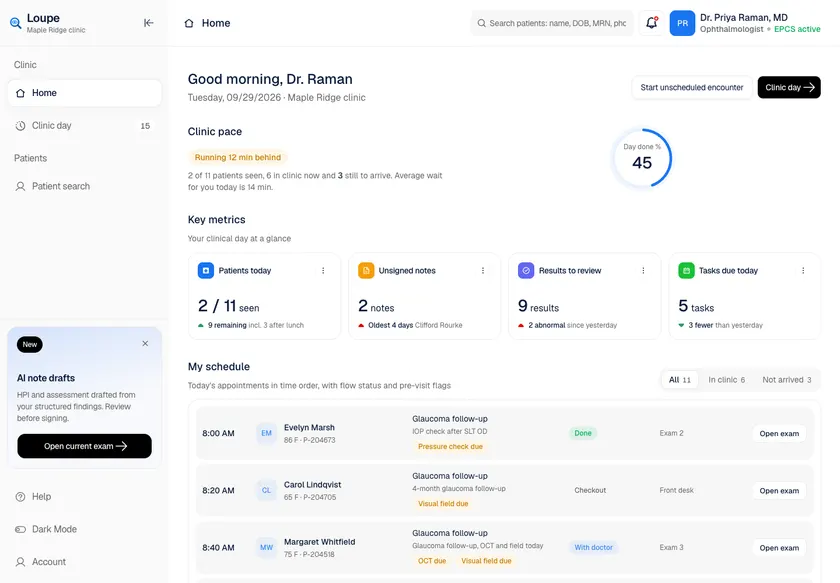
Loupe - Ophthalmology EHR with Per-Eye Charting and Laterality-Aware Coding
Designed and built a clickable ophthalmology EHR for a US eye care group with seven clinics: a clinician's day at a glance, a live patient flow board with dilation timers, patient search with break-the-glass access, a chart summary with right-eye and left-eye findings side by side, and a structured exam workspace per eye.
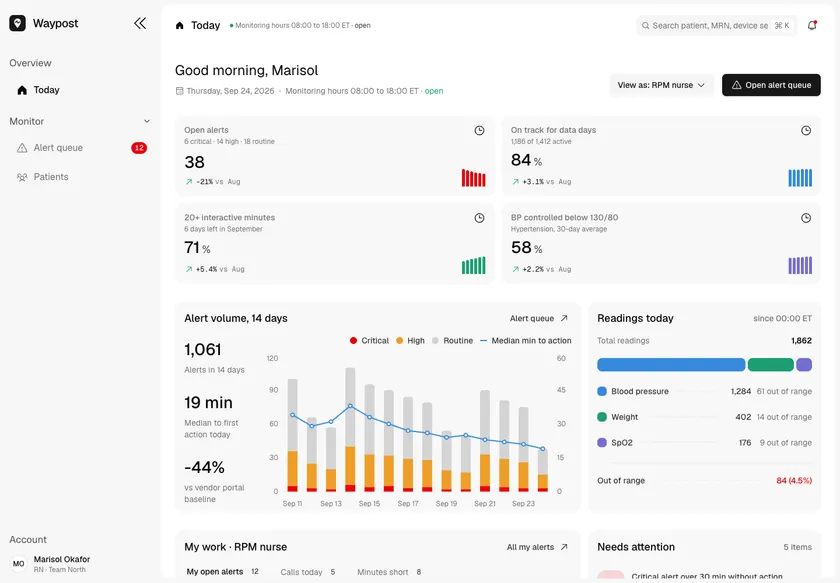
Waypost - Remote Patient Monitoring Platform with Risk-Sorted Alerts
Designed and built a clickable remote patient monitoring platform for a US cardiology and primary care group: home blood pressure, weight and SpO2 readings from cellular devices, a risk-sorted alert queue for nurses, triage with the practice's protocol on screen, and live progress toward each patient's Medicare RPM billing requirements.
