PCI DSS SAQ picker
Say how you take card payments and see which PCI DSS self-assessment questionnaire likely fits, and why.
Free, runs in your browser, no sign-up. Updated 2026-10-25.
Guidance, not legal advice. Your acquirer or the card brands decide which SAQ you may use.
Result
Likely SAQ: SAQ A. Customers are redirected to the provider's payment page, so SAQ A fits. Not legal advice.
Why
- Customers are redirected to the provider's payment page, so SAQ A fits.
Still to do
- SAQ A still includes external vulnerability scans by an Approved Scanning Vendor (ASV) for your e-commerce pages.
| SAQ | Who it is for |
|---|---|
| SAQ A | E-commerce where every element of the payment page comes from a PCI DSS compliant provider (a redirect or the provider's iframe). |
- Your acquirer or the card brands decide which SAQ you may use and whether you must file one at all.
- PCI DSS v4.0.1 is the current version. Its future-dated requirements became mandatory on 31 March 2025.
Send this result to OceanLab
Opens an email to OceanLab with this result and a link to your inputs. Nothing is sent until you press send, and there is no sign-up.
How this is calculated
Service providers get SAQ D for Service Providers, the only SAQ for them. Merchants who store card data electronically get SAQ D for Merchants.
Online: a redirect, or the provider's iframe with script protection confirmed, points to SAQ A. A payment page your own site produces, such as Direct Post, points to SAQ A-EP.
In person: a validated P2PE solution points to SAQ P2PE; standalone approved terminals on IP to SAQ B-IP; a phone or tablet with a secure reader to SAQ SPoC; a virtual terminal on a standalone computer to SAQ C-VT. Anything else falls back to SAQ D.
Each rule comes from a PCI SSC FAQ or announcement linked below. SAQ B and SAQ C are not chosen by the tool because their eligibility text could not be re-checked.
Sources
- PCI SSC FAQ: SAQ A vs SAQ A-EP payment page elements · checked 2026-10-25
- PCI SSC FAQ 1588: SAQ A eligibility criteria for scripts · checked 2026-10-25
- PCI SSC FAQ: who can use SAQ P2PE · checked 2026-10-25
- PCI SSC FAQ: SAQ D is the only SAQ for service providers · checked 2026-10-25
- PCI SSC: what's new with SAQs for PCI DSS v4 · checked 2026-10-25
- PCI SSC bulletin: SAQs for PCI DSS v4.0.1 · checked 2026-10-25
Questions about this tool
Who decides which SAQ I use?
Your acquirer (the bank that processes your card payments) or the card brands. They also decide whether you file an SAQ or need a full assessment.
Does an iframe still qualify for SAQ A?
Under SAQ A for v4.0.1, yes, once you confirm the page is not open to script attacks: with controls such as Requirements 6.4.3 and 11.6.1, or with your PCI DSS compliant provider's confirmation.
Which PCI DSS version applies now?
Version 4.0.1. Version 3.2.1 was retired on 31 March 2024, and the future-dated v4 requirements became mandatory on 31 March 2025.
Is this legal advice?
No. It is a first-pass check to plan engineering work. Confirm it with your acquirer or a QSA.
Other free tools
OceanLab product builds like this
Products OceanLab designed and built. Each case study covers the screens, the scope and the rules it was built for.
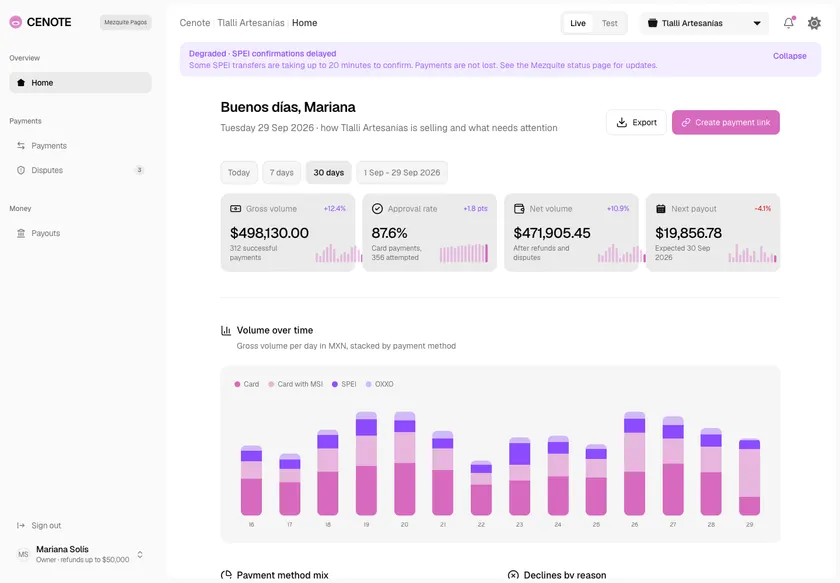
Cenote - Merchant Dashboard for a Mexican Payment Gateway
Designed and built a clickable merchant dashboard for a Mexican online payment gateway that takes cards with meses sin intereses, SPEI transfers and OXXO cash vouchers in MXN: every payment from authorisation to settlement, declines in plain language, refunds with approval limits, chargebacks sorted by deadline and payouts that break down to the last fee.
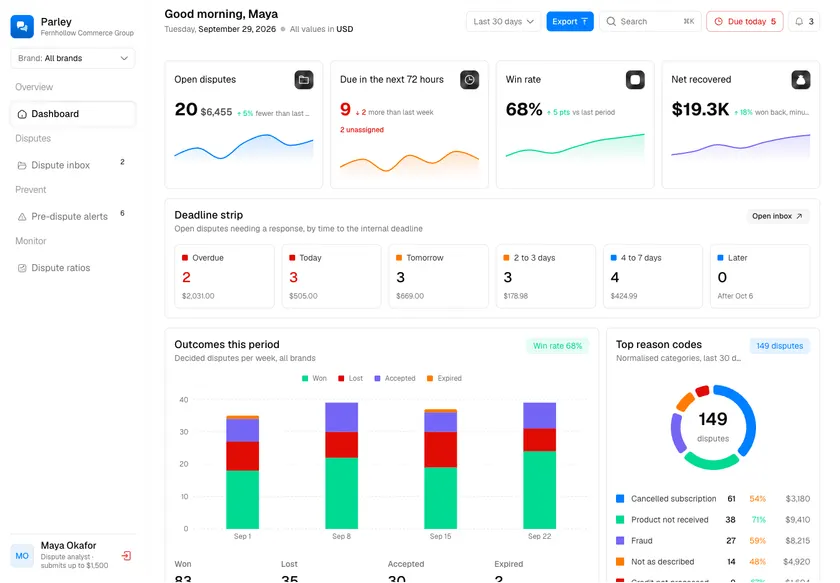
Parley - Chargeback Manager with One Dispute Desk Across Every PSP
Designed and built a clickable chargeback manager for a US merchant group with four online brands on Stripe, Adyen and Braintree: one inbox for every dispute with deadline countdowns, evidence gathered per reason code, a fight or accept recommendation with its reasons, pre-dispute alerts and dispute ratios tracked against network thresholds.
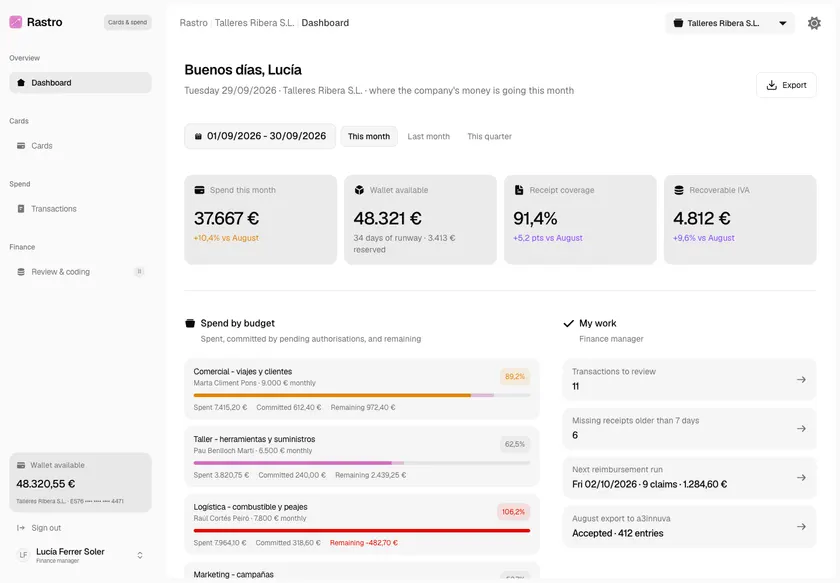
Rastro - Corporate Cards and Spend Management with IVA-Ready Receipts
Designed and built a clickable spend-management platform for a Valencia fintech that gives Spanish SMEs company cards: budgets and card controls checked at authorisation, every transaction matched to its receipt, IVA marked recoverable or not from the invoice type, and a keyboard-driven review queue that turns card spend into bookable entries.
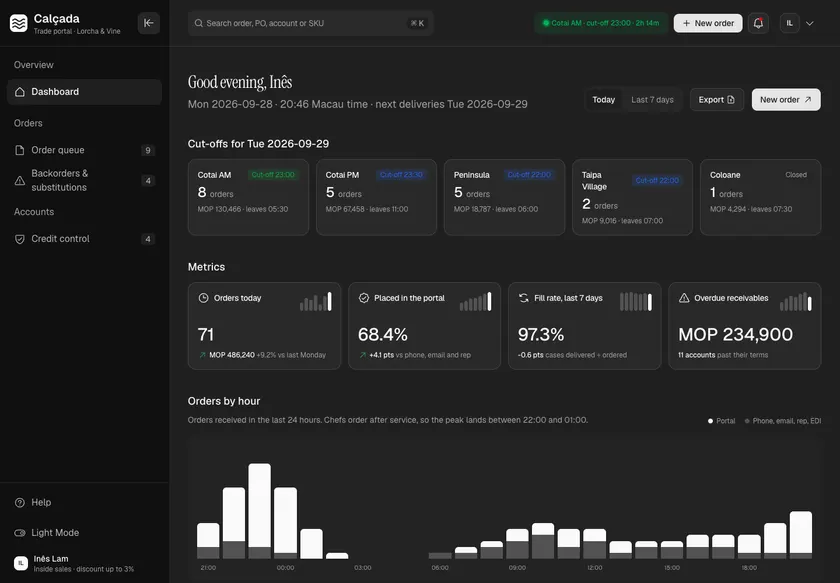
Calçada - B2B Wholesale Portal with Route Cut-offs, Contract Prices and Allergen-Safe Substitutions
Designed and built a clickable staff console for a Macau importer of specialty food and wine that supplies resort outlets, hotels, restaurants, bars and delis: an order queue that puts exceptions first, order detail with the source of every price, shortages resolved with the customer before the truck leaves, and credit holds released with an audited reason.
