Lotse - Open Banking Aggregator Operations Console
PSD2 Account Information Platform for German Banks
Designed and built a clickable operations console for a Hamburg account information service provider that connects fintechs to German bank accounts under PSD2: bank connector health, incidents, and every consent from grant to the 180-day re-authentication.
Most of our work is under NDA. Per agreement, we can share the work but not the company details - all names and identifying information shown here have been changed.
Impact
Operations dashboard, connectors, connector detail with 6 tabs, consent explorer and consent detail, with quick-view panels and action sheets.
Every consent shows its last SCA, the re-authentication due date and the reminders sent 14, 7 and 1 day before; the explorer filters consents due within 7, 14 or 30 days.
The access log counts every background call against the PSD2 limit and keeps calls made with the end user present separate.
1,912 bank codes across 6 banking groups, 26 consents for 8 fintech clients and 10 apps, 6 incidents, with German BICs, BLZ and masked IBANs.
The Problem
Elbtal Konto started with a few hand-built connectors to the largest German banks. With 40 fintech clients and around 1,900 bank connections, the team learned about failing banks from client complaints, re-authentication reminders ran from a cron job nobody owned, consent records sat in three databases, and answering a BaFin request for evidence on one consent took a week. Conversion from "pick a bank" to "connected" had dropped to 61%, and nobody could say where people gave up.
Our Solution
Lotse gives Elbtal Konto's operations, connector and compliance staff one console: a health map of every bank connector by banking group, a connector detail with errors by code and the bank's announced interface changes, a conversion funnel from session start to accounts fetched, and a consent record that shows the grant, the lifecycle, every data access and the 180-day SCA window in one place.
The Challenge: Hundreds of Banks, One Set of Rules
An account information service sits between fintechs, end users and hundreds of German banks, each with its own interface and authentication flow. The operator has to keep every connection working and prove that each consent was granted and used within the rules.
Bank Failures Seen Too Late
Savings banks and cooperative banks are reached through shared platforms, private and direct banks one by one, over Berlin Group NextGenPSD2, other APIs or FinTS. Without per-connector health, a bank's outage only surfaced when a client opened a ticket.
The 180-Day SCA Clock
Under the amended RTS on SCA, banks generally must not ask for SCA again for AISP access for 180 days after the last SCA. After that the end user must re-authenticate, so every consent needs its own clock and reminders that someone owns.
Access Limits and Consent Scope
Without the end user present, an AISP may generally access an account up to four times in 24 hours. Consent is specific to accounts, data, duration and client, and revocation must stop all access immediately.
Evidence for the Regulator
Elbtal Konto is registered with BaFin under the ZAG and falls under GDPR, the BDSG and DORA. Consent records spread across three databases made a single evidence pack for one consent a week of work.
Our Approach: From Rules to a Clickable Console
Spec and Rules Research
Mapped 8 user roles across three audiences (operations, client developers and end users), 36 screens and the data model for connectors, health samples, incidents, connection sessions, consents and the append-only access log. Wrote down the rules the design must follow: PSD2 and the ZAG, the RTS on SCA and its 180-day amendment, the access frequency limit, eIDAS certificates, GDPR, the BDSG and DORA.
Clickable Demo on a Production UI Kit
Built 5 key screens of the operations console on a production dashboard kit: the dashboard with KPIs, a connector health map, the worst 10 connectors, the conversion funnel and the 30-day consent lifecycle; the connector list with 7-day sparklines and a quick view; the connector detail with health, configuration, coverage, changes, incidents and notes; the consent explorer with status pills and re-authentication filters; and the consent detail with grant, lifecycle timeline, access log and data delivered.
What a Production Build Adds
Live connections to bank dedicated interfaces and shared savings and cooperative bank platforms, eIDAS QWAC and QSealC certificates, BaFin, EBA and Bundesbank register checks, KYB and sanctions screening, Postmark for receipts and reminders, Statuspage, Datadog and PagerDuty. Staff roles with audited access, a hash-chained audit log, and the remaining screens: incidents with DORA classification, reminders, categorisation, client onboarding, data subject requests, the developer console and the hosted consent flow.
Why It Works: Health and Consent in One View
Worst Status First
The health map colours each banking group by its worst connector, and a global pill shows how many banks are healthy on every page. Operations staff see a failing bank before a client reports it.
Errors Named by Code
Each connector breaks failures down by code, such as TIMEOUT, SERVICE_UNAVAILABLE or CONSENT_INVALID, next to success rate, p95 response time and daily uptime, so the team can tell a bank outage from a consent problem.
One Record per Consent
Scopes, masked accounts, the consent text version shown, the SCA approach, every renewal and reminder, and each data access with its count against the 4-per-24-hours limit sit on one page, ready for a support question or a BaFin evidence pack.
Sensitive Data Locked by Role
IBANs are masked everywhere, end users appear only by the client's reference, and raw transactions stay locked for the Operations role. Revoking needs a reason, and CSV exports are logged.
Related case studies
View all: Banking & lending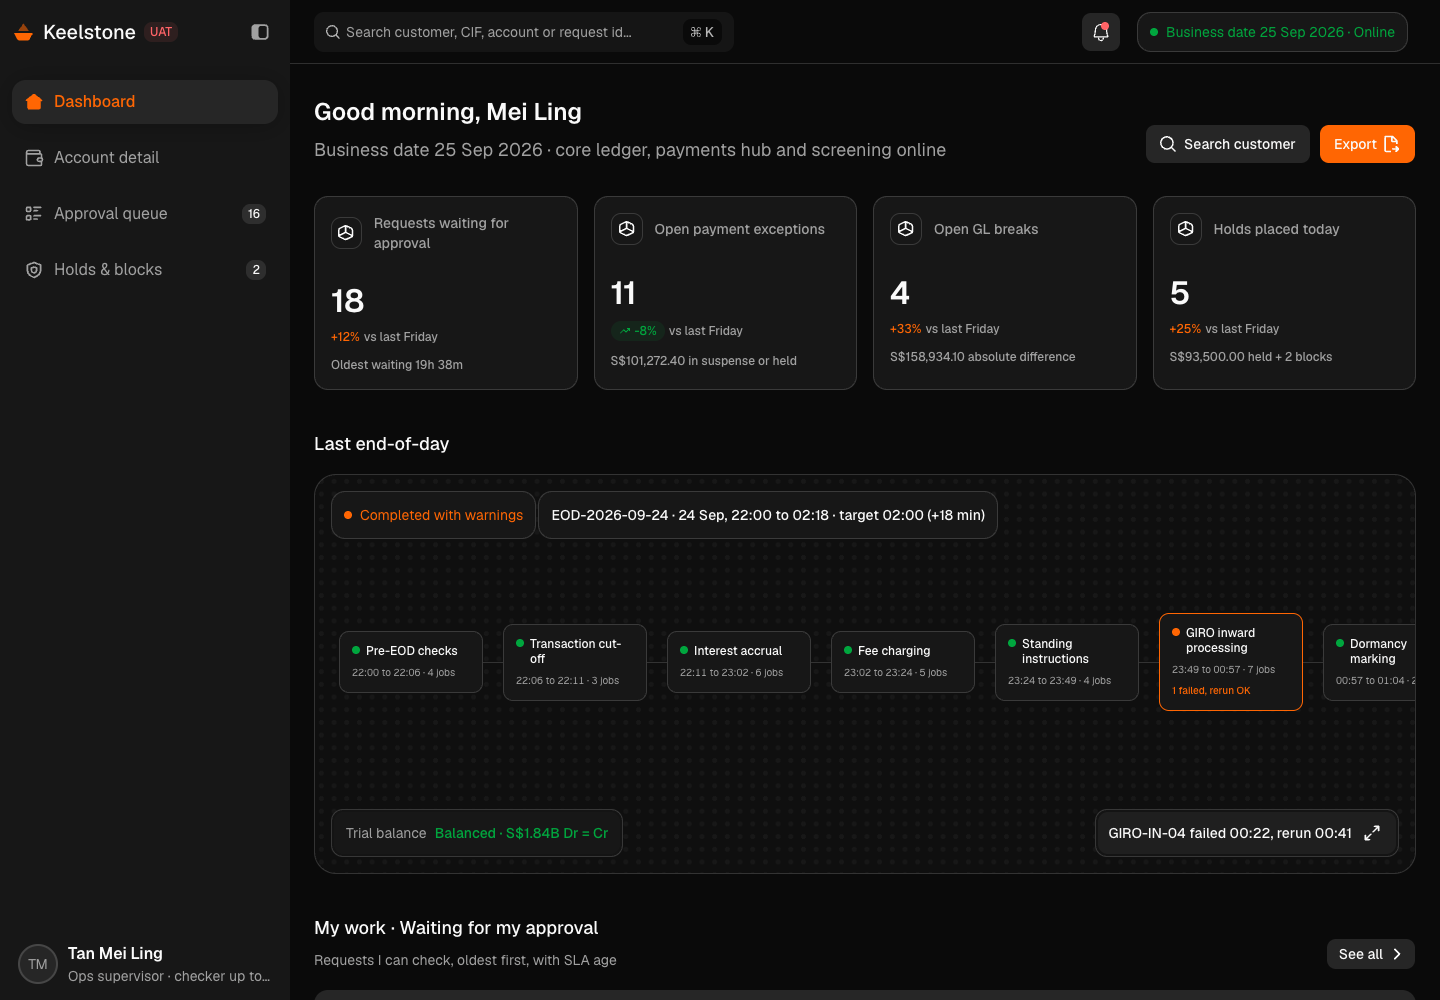
Keelstone - Core Banking Back-Office Console with Maker-Checker
Designed and built a clickable back-office console for a Singapore bank's deposit operations: holds and blocks, limit changes, fee waivers, payment repairs and end-of-day, with every money-moving change going through maker-checker approval.
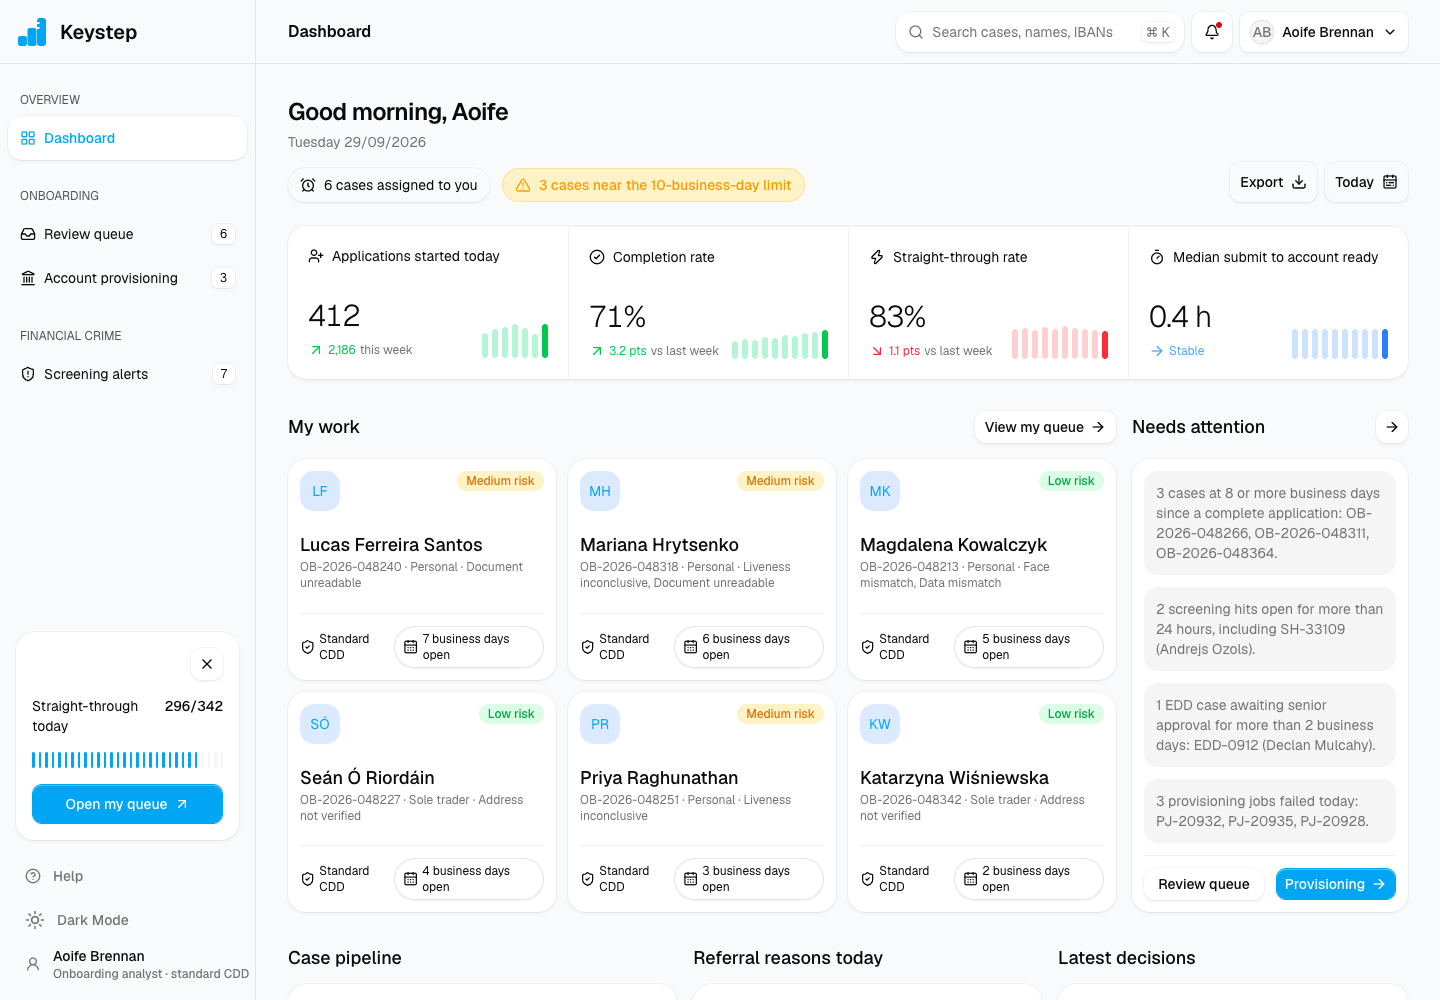
Keystep - Digital Bank Onboarding with ID, Liveness and Risk-Based Review
An onboarding platform for an Irish digital bank: applicants open a EUR current account from their phone with ID and selfie liveness checks, and a staff console lets onboarding and financial crime teams review the cases the rules cannot decide, through to an issued Irish IBAN.
Enterprise Software Engineering - Human + AI
Contact Us
© 2026 - Copyright. All Rights reserved Oceanlab
Location
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center

Enterprise Software Engineering - Human + AI
Contact Us
Locations
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center
© 2026 - Copyright. All Rights reserved Oceanlab