Hradlo - Partner API Gateway Console for a Central European Parcel Carrier
Partner API Gateway for a Czech Parcel Carrier
Designed and built a clickable API gateway console for a Brno parcel carrier whose rates, labels, tracking and pickup APIs serve e-shops, marketplaces and shipping platforms across five countries: partner plans and limits, a request log with personal data redacted before storage, and version retirements with Sunset and Deprecation headers.
Most of our work is under NDA. Per agreement, we can share the work but not the company details - all names and identifying information shown here have been changed.
Impact
Dashboard, partners, partner detail with 8 tabs, the request log with its request detail panel, and versions and deprecation. Every one of the 24 demo partners opens its own page.
Recipient names, phone numbers, emails and street addresses become [REDACTED:...] labels, IBANs keep their last 3 characters, tracking numbers become keyed hashes and Authorization headers are masked. There is no reveal button.
Deprecate version enforces the 180-day minimum, notices go out 90, 30 and 7 days before sunset, and brownouts return 410 Gone to flush out forgotten integrations first.
Partners in 5 countries on 4 plans, 5 API products with 9 versions, 60 logged requests across production and sandbox, 7 webhook subscriptions and 8 staff users.
The Problem
Veveří Parcel's integration team issued API keys by email from a spreadsheet. Keys never expired, large partners shared one key across a dozen developers, and when a marketplace's bug sent 40 times its usual label traffic during the pre-Christmas peak, the only lever was blocking its IP at the firewall. Logs held recipients' names, phones and addresses in full, retiring the old tracking API took 14 months, and high-volume billing was worked out by hand each month.
Our Solution
Hradlo decides who may call which API, how often and on which version. Partner managers see every partner's plan, limits, quota and deprecated calls in one place, support engineers inspect any request without seeing personal data, and product managers retire versions on a published schedule that tells partners in the response headers.
The Challenge: Opening Shipping APIs Without Losing Control
About 1,400 partners call the carrier's APIs to quote, label, track and book pickups. Every call can carry a recipient's personal data, a few partners produce most of the traffic, and a carrier of this size is likely in scope for NIS2.
Personal Data in Every Request
Parcel requests carry recipients' names, addresses, phone numbers and emails. GDPR data minimisation and storage limitation mean personal fields have to be removed before a log is stored, while support still needs enough of the call to debug it.
One Partner Can Swamp the Gateway
A single marketplace bug sent 40 times the usual label traffic at peak. Limits have to be set per partner and per API product, raised for real events with an expiry, and enforced with 429 and Retry-After rather than a firewall block.
Nobody Knew Who Called Old Versions
Retiring the old tracking API took 14 months because nobody could list the partners still calling it. Retirement needs dates, a successor, a migration guide and a count of remaining callers, announced with the Sunset (RFC 8594) and Deprecation (RFC 9745) headers.
Access Control Under NIS2
Postal and courier services fall under NIS2, which Czechia transposed through a new Cybersecurity Act supervised by NÚKIB. Partner access needs strong authentication with OAuth 2.0 client credentials, IP allowlists, mutual TLS for the largest partners and fast revocation.
Our Approach: From Gateway Rules to a Clickable Console
Spec and Rules Research
Mapped 10 roles across staff, partner console and public onboarding, 34 screens, and the data model for partners, plans, limit overrides, apps, credentials, request logs, redaction rules, versions, webhooks, incident banners and billing. Wrote down the rules the design follows: GDPR, NIS2 and the Czech Cybersecurity Act, OAuth 2.0 and mTLS, the Sunset and Deprecation headers, 429 with Retry-After and Problem Details, and secrets shown once and stored only as hashes.
Clickable Demo on a Production UI Kit
Built 5 key screens on a production dashboard kit with a Production and Sandbox switcher: the dashboard with KPIs, traffic by API product, top partners and a needs-attention list; partners with filters and a quick view; partner detail with plan changes, limit overrides, suspend and offboard; the request log with timeline, masked headers and redacted bodies; and versions with the deprecation timeline, schedule and brownouts. All actions run on local state.
What a Production Build Adds
Integration with the gateway data plane (Envoy or Kong), Keycloak for client credentials, HashiCorp Vault for secrets and the mTLS certificate authority, ClickHouse for logs and analytics, ARES and VIES at onboarding, Microsoft Entra ID sign-on, partner email, PagerDuty and the invoicing export. Redaction running on the gateway node before logs leave it, a hash-chained audit log, second approvers for sensitive changes, and the 29 remaining screens including the partner console.
Why It Works: Control Without Exposing Data
Redaction Happens Before Storage
Request bodies show [REDACTED:phone] and similar labels with the rules that fired, and authorization values are masked. Searching a tracking number matches a keyed hash and says so, and copy as cURL uses a placeholder credential.
Limits With a Reason and an Expiry
Each override on the partner page shows who set it, why and when it expires, and an override above 2x the plan asks for a second approver. Quota bars turn amber above 80% and red above 95%, so a partner heading for its limit is visible before it is throttled.
Retirements Nobody Is Surprised By
The versions timeline marks today and hatches deprecated periods, the schedule lists partners still calling with their 7-day call counts, and the headers preview shows exactly what the gateway adds to responses. Partners at risk get a reminder in one click.
Production Is Hard to Mistake
The environment switcher scopes every figure, and Production puts a red edge on the sidebar. Live incident banners sit under the top bar on every page, and affected responses carry an X-VP-Notice header pointing to the banner.
Related case studies
View all: Developer tools & APIs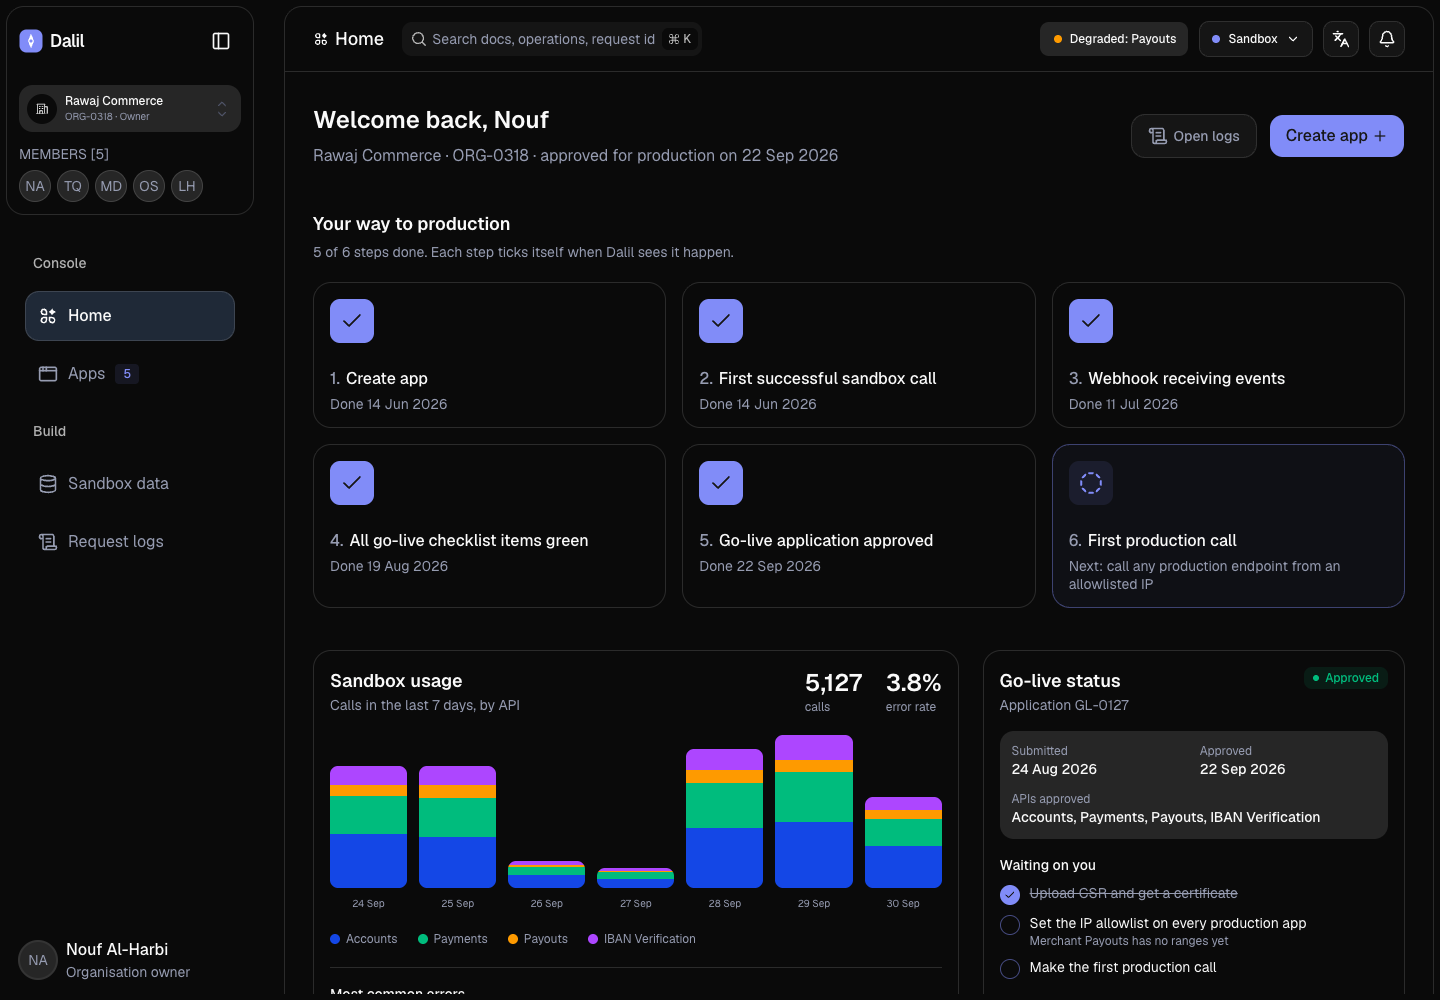
Dalil - Bilingual Developer Portal for a Saudi Payments API
Designed and built a clickable developer console for a Riyadh payments and open banking fintech: a journey tracker from first sandbox call to production, app credentials with shown-once secrets, keys and mTLS certificates, synthetic sandbox data with scenario switches, and request logs that explain each error in plain words.
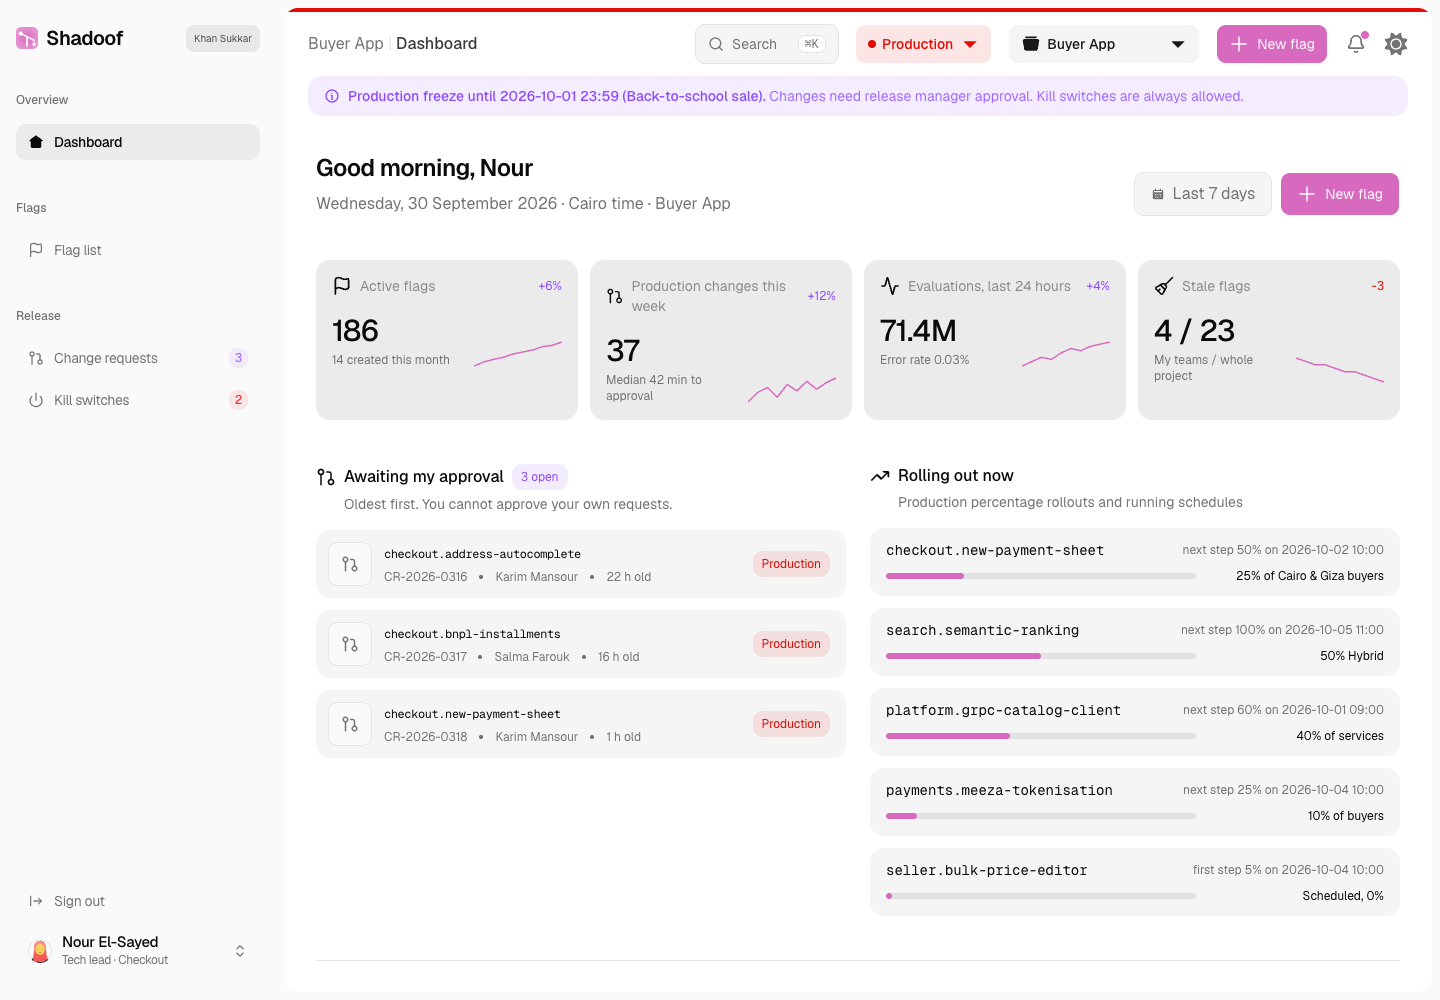
Shadoof - Feature Flag and Progressive Delivery Service for a Marketplace's Engineering Teams
Designed and built a clickable feature flag console for the engineering teams of a Cairo online marketplace: targeting rules and sticky percentage rollouts per environment, change requests with a second approver for Production, kill switches for incidents and a full change history for every flag.
Enterprise Software Engineering - Human + AI
Contact Us
© 2026 - Copyright. All Rights reserved Oceanlab
Location
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center

Enterprise Software Engineering - Human + AI
Contact Us
Locations
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center
© 2026 - Copyright. All Rights reserved Oceanlab