Dalil - Bilingual Developer Portal for a Saudi Payments API
Developer Portal for a Saudi Open Banking Fintech
Designed and built a clickable developer console for a Riyadh payments and open banking fintech: a journey tracker from first sandbox call to production, app credentials with shown-once secrets, keys and mTLS certificates, synthetic sandbox data with scenario switches, and request logs that explain each error in plain words.
Most of our work is under NDA. Per agreement, we can share the work but not the company details - all names and identifying information shown here have been changed.
Impact
Console home, apps, app detail, sandbox data and request logs. Each of the 9 demo apps, 7 sandbox and 2 production, opens its own detail page with credentials, redirect URIs, scopes, webhooks and activity tabs.
A client secret is shown in full only when it is generated and then kept as its last 4 characters. Up to two can be active, so a rotation needs no downtime, and a third is blocked until one is revoked.
Reject the next consent, fail the next payment with a chosen error, delay webhooks or make the test bank unavailable. Testing them counts toward the go-live technical checklist.
6 personas with English and Arabic names, 26 accounts on test IBANs with the reserved bank code 99, 156 transactions and 18 consents, plus 30 request logs and 5,127 sandbox calls over 7 days.
The Problem
Wadi Sahba's API docs were a PDF emailed after a sales call and a Postman collection two versions behind the real API. A support engineer created sandbox credentials by hand and sent them over WhatsApp, the Arabic docs translated an older English release, and going live meant a long email thread with compliance, spreadsheets of KYB documents and a manual certificate exchange. A typical integrator took 7 to 10 weeks from first contact to first live call.
Our Solution
Dalil gives every integrator one place to go from first sandbox call to production. The developer console tracks each step of the journey, creates apps with secrets, public keys and mTLS certificates handled safely, seeds a realistic synthetic sandbox with switches to break things on purpose, and shows every request with the error explained.
The Challenge: Open Banking Integrations in Two Languages
Wadi Sahba sells Accounts, Payments, Payouts and IBAN Verification APIs under the SAMA Open Banking Framework. Its portal has to teach developers in Arabic and English, keep credentials and customer data safe, and hand compliance a clean application before any live credentials are issued.
Credentials Sent by Hand
Sandbox secrets were created by a support engineer and sent in chat. Production uses OAuth 2.0 with signed client authentication and certificate-bound tokens over mutual TLS, so secrets, public keys and certificates each need their own safe flow.
A Sandbox That Never Fails
Developers need realistic customers, accounts and consents to build against, but no real customer or IBAN may ever appear. They also need to see consent rejections, failed payments and unavailable banks before they meet them in production.
Debugging Without Customer Data
Sandbox calls can be shown in full to help a developer debug, but production request bodies carry customer data. Personal data under the PDPL has to stay minimal and in the Kingdom.
Going Live Through Compliance
Each production applicant is checked as a business customer: commercial registration, VAT, national address, authorised signatory, beneficial owners and sanctions and PEP screening under the Saudi Anti-Money Laundering Law. That check ran on email and spreadsheets.
Our Approach: From Open Banking Rules to a Clickable Console
Spec and Rules Research
Mapped 10 user roles across developers and Wadi Sahba staff, 35 screens (10 public pages, 11 developer console and 14 admin console screens) and the data model for organisations, apps, secrets, certificates, webhooks, request logs, sandbox test users and consents, spec versions, docs pages and go-live applications. Wrote down the rules the design follows: the SAMA Open Banking Framework and its phases, the SAMA regulatory sandbox, the PDPL, a FAPI-based security profile with mTLS and private_key_jwt, KYB under the Saudi AML Law, and Arabic as a first-class language with a Sunday to Thursday working week.
Clickable Demo on a Production UI Kit
Built the developer console's 5 key screens on a production dashboard kit, as seen by an organisation owner already approved for production: console home with the journey tracker, sandbox usage and go-live status, apps by environment, app detail with secrets, keys, certificates, webhooks and IP allowlist, sandbox data with test users and scenario switches, and request logs with a detail panel. Creating apps, generating and revoking secrets and arming scenarios all run on local state.
What a Production Build Adds
The public docs and API reference with try-it, generated from OpenAPI, in full right-to-left Arabic; the go-live wizard and the admin console where analysts review each application and a different compliance officer approves it. Integrations with Wathq for commercial registration, the Saudi Post National Address API, Nafath, sanctions and PEP screening, e-signature, SMS, in-Kingdom docs search, GitHub spec imports, translation memory and the issuing CA, a contract with the API gateway, and an append-only audit log. The FAPI version is confirmed against the SAMA technical standards in force.
Why It Works: A Visible Path from Sandbox to Production
The Journey Ticks Itself
Console home shows six steps from creating an app to the first production call, each ticked with its date when Dalil sees it happen. The go-live card lists what is still waiting on the developer, and the changelog panel shows only deprecations and breaking changes for operations the organisation actually called.
Secrets Never Stay Readable
Client secrets are shown once and then only by their last 4 characters. Private keys never leave the developer's machine: the app takes a public JWK or a JWKS URL, and production certificates are issued from a certificate signing request.
Sandbox and Production Never Blur
Production stays greyed out with Apply to go live until the organisation is approved, and a red band marks every production page. Production apps come only from a go-live approval, their scopes are read-only with Request change, and their logs keep metadata only.
Errors Explain Themselves
The sandbox log panel shows masked headers and bodies with the error in plain words, such as an expired client assertion or a reused idempotency key, and the fix. Scenario switches let a developer trigger those failures on purpose against synthetic data.
Related case studies
View all: Developer tools & APIs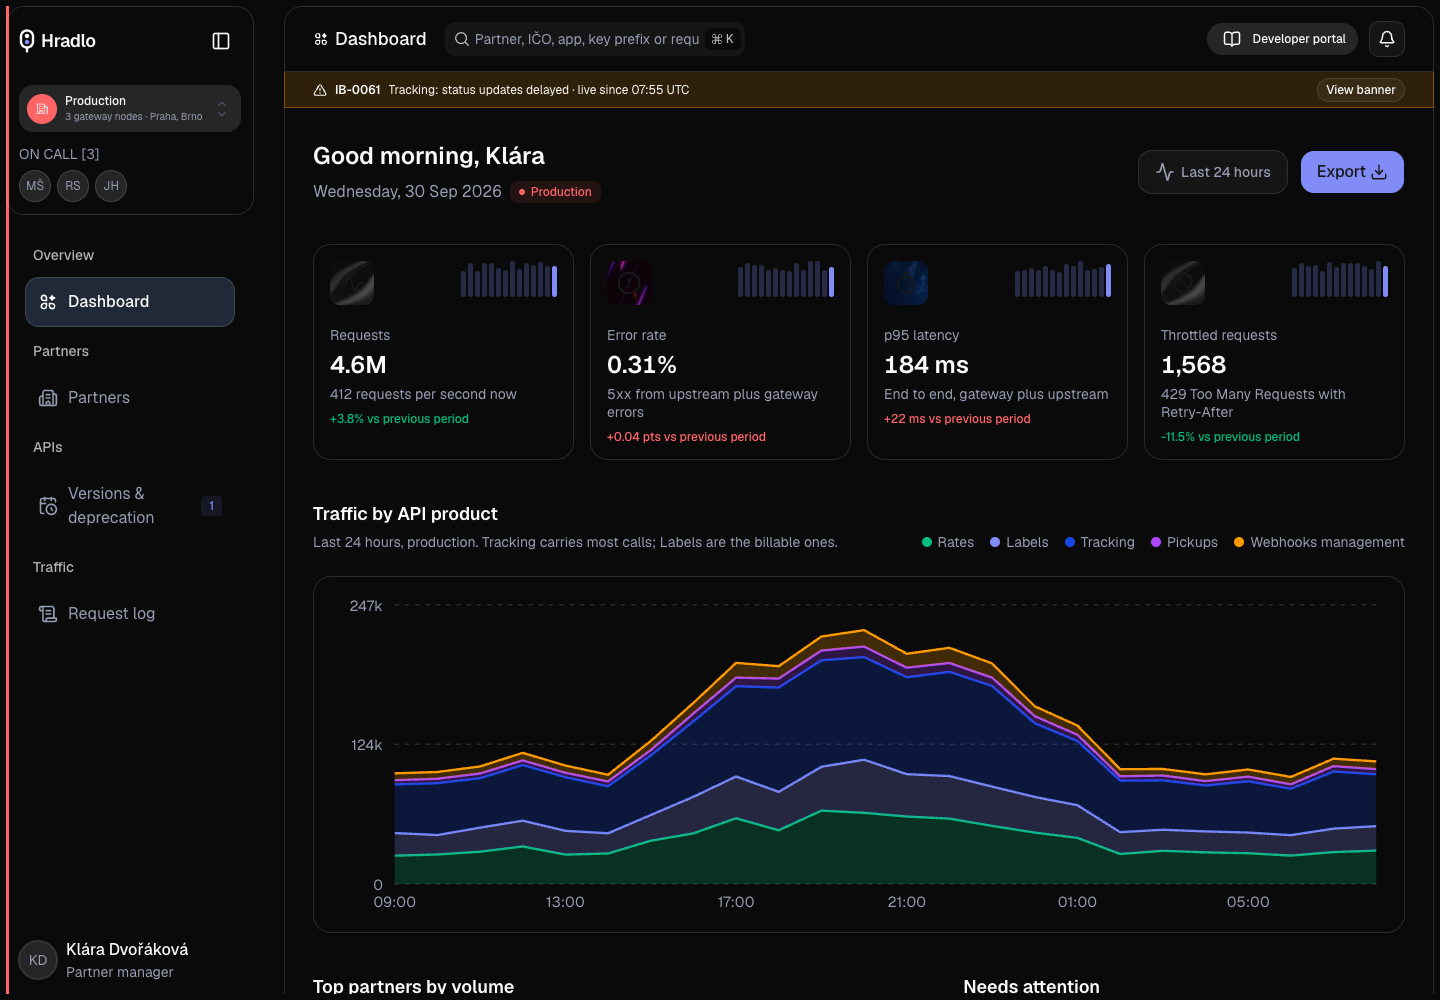
Hradlo - Partner API Gateway Console for a Central European Parcel Carrier
Designed and built a clickable API gateway console for a Brno parcel carrier whose rates, labels, tracking and pickup APIs serve e-shops, marketplaces and shipping platforms across five countries: partner plans and limits, a request log with personal data redacted before storage, and version retirements with Sunset and Deprecation headers.
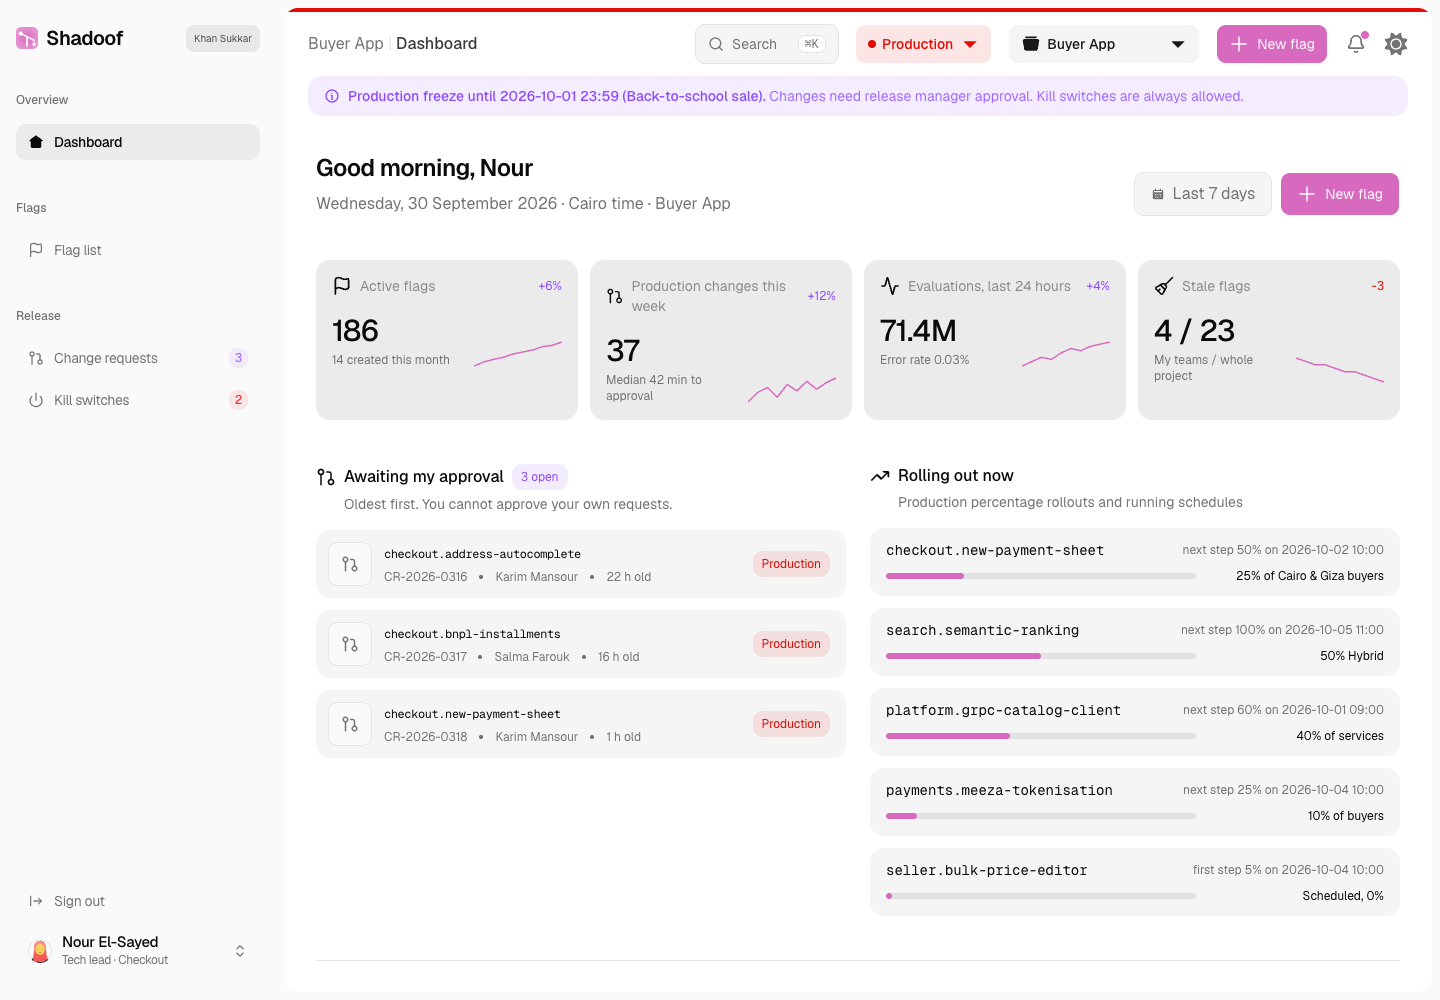
Shadoof - Feature Flag and Progressive Delivery Service for a Marketplace's Engineering Teams
Designed and built a clickable feature flag console for the engineering teams of a Cairo online marketplace: targeting rules and sticky percentage rollouts per environment, change requests with a second approver for Production, kill switches for incidents and a full change history for every flag.
Enterprise Software Engineering - Human + AI
Contact Us
© 2026 - Copyright. All Rights reserved Oceanlab
Location
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center

Enterprise Software Engineering - Human + AI
Contact Us
Locations
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center
© 2026 - Copyright. All Rights reserved Oceanlab