Hengert - Trust and Safety Console for an End-to-End Encrypted Messenger
Operator Console for a Swiss Family Messenger
Designed and built a clickable operator console for a Zurich company's end-to-end encrypted messenger for families and small groups: an abuse report queue worked only from content users chose to forward, account pages that list what the server holds and what it does not, and a law enforcement desk that answers only with data that exists.
Most of our work is under NDA. Per agreement, we can share the work but not the company details - all names and identifying information shown here have been changed.
Impact
Overview, abuse report queue, report detail, account search, account detail and law enforcement requests with a request drawer. Every one of the 18 demo reports opens its own detail view.
Staff see account metadata and content a reporter chose to forward, nothing else. A fixed strip on every page says so, and each account page lists what the server does not hold.
Report age tags turn amber after 12 hours and red after 24. Child safety and violent threat reports become P1 automatically, and a permanent ban waits for the trust and safety lead's approval.
18 abuse reports across 7 reasons, 12 law enforcement requests from Swiss and foreign authorities, 2 preservation holds and 7 operators in 4 roles.
The Problem
Sihlweid's founders saw families in Switzerland and neighbouring countries splitting their chats across three or four apps, and parents wanted a messenger whose operator could not read their messages, with servers in Switzerland. The first prototype was built on a generic chat SDK that kept message content on the server, which made the privacy promise untrue. Hengert is the rebuild: the server routes encrypted envelopes and forgets them.
Our Solution
Hengert's operator console gives Sihlweid's trust and safety agents, lead and legal officers one place to work abuse reports, look up accounts and answer official requests, designed around the small amount of metadata the server still keeps. Agents decide from forwarded content and account metadata, and legal officers answer each request field by field, with a line for everything that is not held.
The Challenge: Running a Messenger You Cannot Read
Hengert uses the Signal Protocol, so message content, group membership, profile names and contact lists live only on members' devices. The operator still has to stop abuse, protect children and answer the authorities, using only what the server holds.
Moderation Without Message Content
Content cannot be scanned. Agents work only from what a reporter forwards, up to 20 messages under client policy, and Hengert cannot verify that a modified app did not alter it. Spam and bot waves have to be found from metadata such as sign-up bursts and message request acceptance rates.
Requests for Data That Does Not Exist
Swiss surveillance law (BÜPF, in English SCPT) can oblige messaging providers to hand over the data they have, with requests arriving through the PTSS. Orders often ask for message content, contacts or group membership, which the server never holds, and every answer has to say exactly that.
Children in a Family Messenger
Hengert is aimed at families, so children will use it, with a client policy minimum age of 13. Child sexual abuse material that reaches the console through a report must go to the trust and safety lead and to the authorities under a written procedure, and agents must never view it.
Privacy Law on Every Field
The revised Swiss data protection act (revFADP) expects privacy by design and by default and a data protection impact assessment for high-risk processing, and the GDPR applies where the service is offered in the EU. Every console view and action has to be justified and recorded.
Our Approach: From a Privacy Table to a Clickable Console
Spec and Rules Research
Mapped 7 roles and 38 screens: 24 member app screens, 12 operator console screens and 2 public web pages. Wrote a fixed table of what the server can and cannot see, then the data model for server-held account and device metadata, device-only data, abuse reports, account actions, appeals, signal rules, law enforcement requests and preservation holds. Wrote down the rules the design follows: the revFADP and its ordinance, BÜPF and the PTSS process, the GDPR for EU users, child safety handling and the Signal Protocol through libsignal.
Clickable Demo on a Production UI Kit
Built the operator console's 6 key screens on a production support-desk kit: the overview with 4 KPIs, reports by reason and a needs attention list, the report queue with tabs, reason filter and age tags, report detail with pick up, take action, no action, escalate and report to authorities, account search and account detail with lift restriction, and the law enforcement desk with a legal review checklist, a per-account data summary and countersign. Actions run on local demo state.
What a Production Build Adds
The member apps for iOS, Android and desktop on libsignal with sealed sender, safety numbers and encrypted backups, SMS verification through Twilio Verify or Vonage Verify, content-free push through APNs and FCM, self-hosted call relays and Swiss hosting such as Exoscale or Infomaniak. Staff SSO with hardware-key two-factor, an audit entry for every console action, the remaining console screens (appeals, spam and bot signals, service health, app versions, settings), and counsel review of Hengert's BÜPF classification and a data protection impact assessment.
Why It Works: Honest About What It Holds
The Console Says What It Cannot See
Every account page shows what the server holds next to a fixed list of what it does not: messages, contacts, groups, profile name and photo, call logs and backups. There is no read messages action because none exists, so agents never promise what cannot be given.
Forwarded Content, Clearly Labelled
Each forwarded message shows its time by the reporter's clock and a note that Hengert cannot verify it was not altered. Sensitive media stays hidden until the agent clicks to reveal, and child safety media is never shown, only its hash.
Answers Only From What Exists
A request's data summary lists the held fields for each named account and a Not held by Hengert line for everything else asked. A second legal officer countersigns before anything is sent, and the page keeps the half-yearly counts for the transparency report.
The Most Urgent Report Comes First
Needs attention lists child safety reports first, then reports over 24 hours, legal deadlines and incidents. The reporter's account id and age are shown to the agent but never to the reported person, and a permanent ban waits for the lead.
Related case studies
View all: Social & community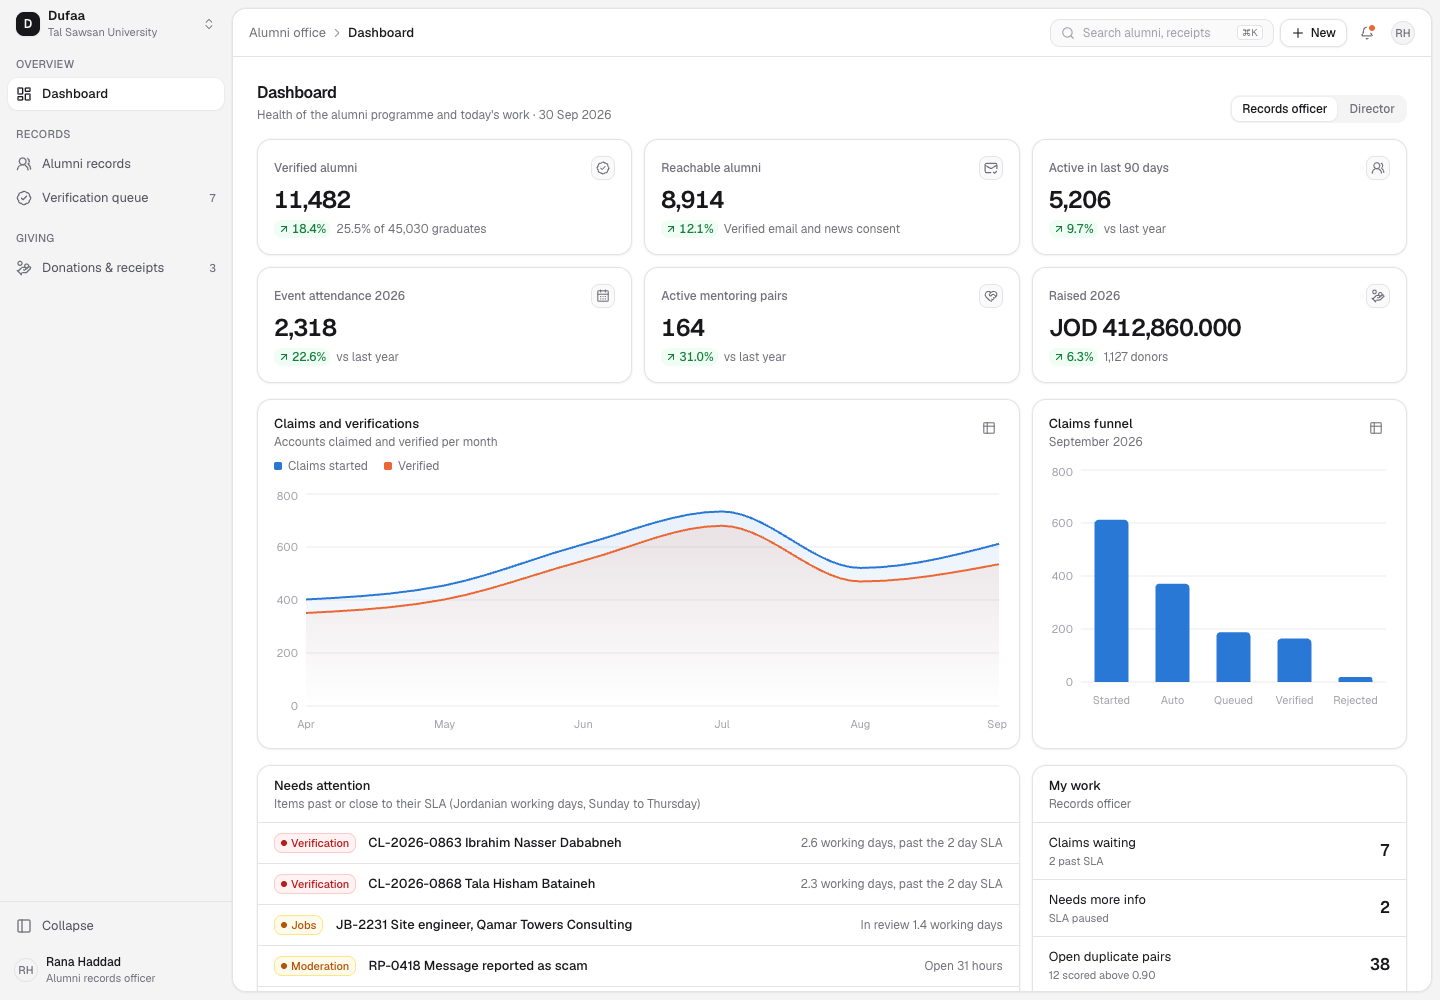
Dufaa - Alumni Network Console with Arabic and Latin Record Matching
Designed and built a clickable alumni office console for a private university in Amman with about 45,000 graduates in more than 60 countries: verify account claims against registrar records in Arabic and Latin script, keep one clean record per graduate with per-field privacy, and issue a numbered official receipt for every gift.
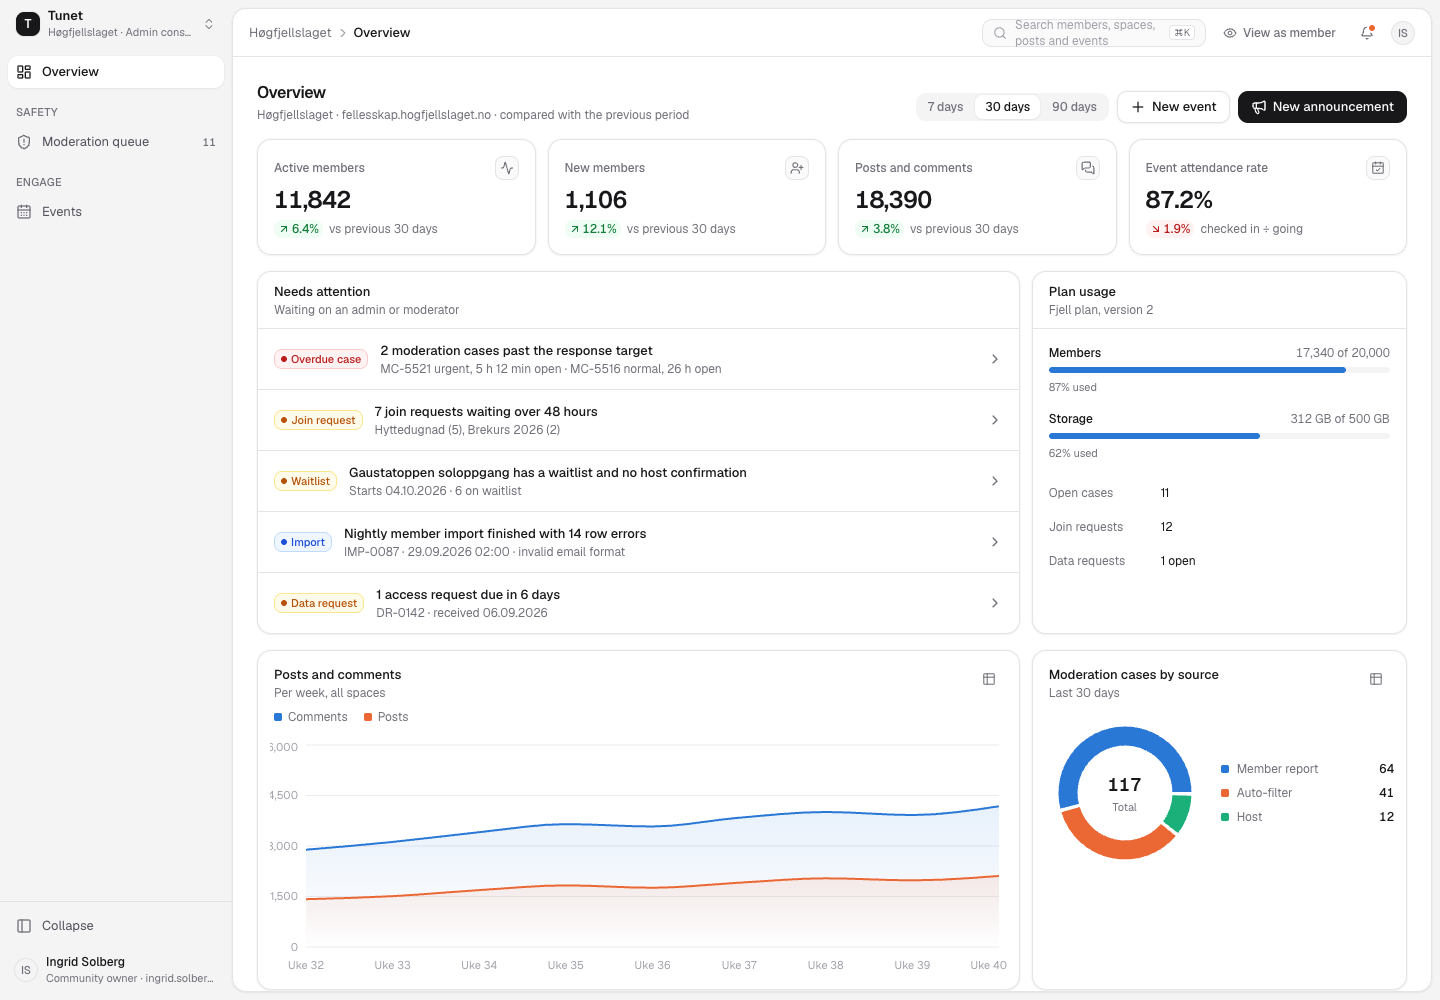
Tunet - White-Label Community Platform for Membership Organisations
Designed and built a clickable community admin console for an Oslo software company's white-label community platform, shown for its first customer, a national hiking association: a community overview, a moderation queue with a full case workspace and decision flow, and event management with RSVPs, waitlist, check-in and attendee messages.
Enterprise Software Engineering - Human + AI
Contact Us
© 2026 - Copyright. All Rights reserved Oceanlab
Location
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center

Enterprise Software Engineering - Human + AI
Contact Us
Locations
Global Headquarters
21 Merchant Road, 3rd Floor, Singapore 058267
Main corporate office and leadership operations
North America Office
548 Market Street, PMB 12345, San Francisco, CA 94104
Client operations and business development
India Office
402 Shivalik Shilp II, SG Highway, Ahmedabad 380015
Engineering and delivery center
© 2026 - Copyright. All Rights reserved Oceanlab